

Try 350-701 Exam Valid Dumps with Instant Download Free Updates
350-701 Dumps First Attempt Guaranteed Success
NEW QUESTION # 97
An organization wants to secure users, data and applications m the cloud. The solution must be API-based and operate as a cloud-native CASB Which solution must be used for this implementation?
- A. Cisco Firepower Next-Generation Firewall
- B. Cisco Cloudlock
- C. Cisco Cloud Email Security
- D. Cisco Umbrella
Answer: B
NEW QUESTION # 98
Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?
- A. Cisco Talos Intelligence
- B. Encrypted Traffic Analytics
- C. Cognitive Threat Analytics
- D. Threat Intelligence Director
Answer: D
NEW QUESTION # 99
What are two rootkit types? (Choose two)
- A. bootloader
- B. user mode
- C. registry
- D. buffer mode
- E. virtual
Answer: A,B
NEW QUESTION # 100
What is managed by Cisco Security Manager?
- A. ASA
- B. access point O
- C. WSA
- D. ESA
Answer: A
Explanation:
https://www.cisco.com/c/en/us/products/collateral/security/security-manager/datasheet-C78-737182.html
NEW QUESTION # 101
Which functions of an SDN architecture require southbound APIs to enable communication?
- A. SDN controller and the network elements
- B. SDN controller and the cloud
- C. management console and the cloud
- D. management console and the SDN controller
Answer: A
Explanation:
The Southbound API is used to communicate between Controllers and network devices
NEW QUESTION # 102
Which two request methods of REST API are valid on the Cisco ASA Platform? (Choose two.)
- A. PUSH
- B. GET
- C. PUT
- D. OPTIONS
- E. CONNECT
Answer: B,C
NEW QUESTION # 103
What is a benefit of using Cisco Tetration?
- A. It collects policy compliance data and process details.
- B. It collects enforcement data from servers and collects interpacket variation.
- C. It collects near-real time data from servers and inventories the software packages that exist on servers.
- D. It collects telemetry data from servers and then uses software sensors to analyze flow information.
Answer: B
NEW QUESTION # 104
A Cisco ESA network administrator has been tasked to use a newly installed service to help create policy based on the reputation verdict. During testing, it is discovered that the Cisco ESA is not dropping files that have an undetermined verdict. What is causing this issue?
- A. The file has a reputation score that is above the threshold
- B. The file has a reputation score that is below the threshold
- C. The policy was created to send a message to quarantine instead of drop
- D. The policy was created to disable file analysis
Answer: D
Explanation:
Maybe the "newly installed service" in this question mentions about Advanced Malware Protection (AMP) which can be used along with ESA. AMP allows superior protection across the attack continuum.
+ File Reputation - captures a fingerprint of each file as it traverses the ESA and sends it to AMP's cloudbased intelligence network for a reputation verdict. Given these results, you can automatically block malicious files and apply administrator-defined policy.
+ File Analysis - provides the ability to analyze unknown files that are traversing the ESA. A highly secure sandbox environment enables AMP to glean precise details about the file's behavior and to combine that data with detailed human and machine analysis to determine the file's threat level. This disposition is then fed into AMP cloud-based intelligence network and used to dynamically update and expand the AMP cloud data set for enhanced protection
NEW QUESTION # 105
Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.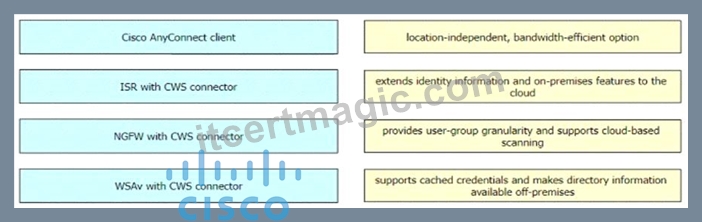
Answer:
Explanation:
Explanation:
Reference:
https://www.westconcomstor.com/medias/CWS-data-sheet-c78-729637-1-.pdf?context=bWFzdGVyfHJvb3R8M
NEW QUESTION # 106
A network engineer must configure a Cisco ESA to prompt users to enter two forms of information before gaining access The Cisco ESA must also join a cluster machine using preshared keys What must be configured to meet these requirements?
- A. Enable two-factor authentication through a TACACS+ server and then join the cluster by using the Cisco ESA GUI.
- B. Enable two-factor authentication through a RADIUS server and then join the cluster by using the Cisco ESA GUI
- C. Enable two-factor authentication through a TACACS+ server and then join the cluster by using the Cisco ESA CLI
- D. Enable two-factor authentication through a RADIUS server and then join the cluster by using the Cisco ESA CLI.
Answer: D
NEW QUESTION # 107
Which IETF attribute is supported for the RADIUS CoA feature?
- A. 30 Calling-Station-ID
- B. 24 State
- C. 42 Acct-Session-ID
- D. 81 Message-Authenticator
Answer: B
NEW QUESTION # 108
Refer to the exhibit.
What is the result of this Python script of the Cisco DNA Center API?
- A. adds a switch to Cisco DNA Center
- B. deletes a switch from Cisco DNA Center
- C. adds authentication to a switch
- D. receives information about a switch
Answer: D
Explanation:
The Python script of the Cisco DNA Center API in the exhibit uses the requests module to send a GET request to the /dna/intent/api/v1/network-device endpoint, which returns a list of network devices managed by Cisco DNA Center. The script also uses HTTPBasicAuth to provide the username and password for authentication. The script then parses the JSON response and prints the hostname, type, management IP address, and software version of each device in a table format using the prettytable module. Therefore, the result of this script is to receive information about a switch or switches from Cisco DNA Center. References:
* Python Scripting APIs in Cisco DNA Center Let You Improve Effectiveness, Topic: Network device's script, simple and easy to create
* Intro to Cisco DNA Center REST API with Python, Module 2: Using Python to Retrieve a Network Device List
* Cisco DNA Center API Call Python Script Example, Topic: Cisco DNA CENTER SANDBOX Call DNA Center API Call Python Script Example
NEW QUESTION # 109
An engineer wants to automatically assign endpoints that have a specific OUI into a new endpoint group.
Which
probe must be enabled for this type of profiling to work?
- A. SNMP
- B. DHCP
- C. NMAP
- D. NetFlow
Answer: C
Explanation:
Reference:
http://www.network-node.com/blog/2016/1/2/ise-20-profiling
NEW QUESTION # 110
An attacker needs to perform reconnaissance on a target system to help gain access to it. The system has weak passwords, no encryption on the VPN links, and software bugs on the system's applications. Which vulnerability allows the attacker to see the passwords being transmitted in clear text?
- A. unencrypted links for traffic
- B. improper file security
- C. weak passwords for authentication
- D. software bugs on applications
Answer: A
NEW QUESTION # 111
An organization is receiving SPAM emails from a known malicious domain. What must be configured in order to prevent the session during the initial TCP communication?
- A. Configure the Cisco ESA to drop the malicious emails
- B. Configure policies to stop and reject communication
- C. Configure policies to quarantine malicious emails
- D. Configure the Cisco ESA to reset the TCP connection
Answer: D
NEW QUESTION # 112
What are two workloaded security models? (Choose two)
- A. PaaS
- B. SaaS
- C. IaaS
- D. off-premises
- E. on-premises
Answer: C,E
Explanation:
Workloaded security models are ways of protecting applications, services, and capabilities that run on a cloud resource. Virtual machines, databases, containers, and applications are all considered cloud workloads. There are different types of cloud deployment models, such as public, private, hybrid, and multicloud. Depending on the deployment model, the cloud workload security can vary in terms of responsibility, visibility, and control.
Infrastructure as a service (IaaS) is a cloud deployment model where the cloud provider offers the basic computing infrastructure, such as servers, storage, and networking, as a service. The customer is responsible for installing, configuring, and managing the operating systems, applications, and security of the workloads that run on the cloud infrastructure. IaaS provides the customer with more flexibility and control over the workload security, but also more complexity and overhead.
On-premises is a deployment model where the customer owns and operates the entire IT infrastructure, including the hardware, software, and security. The customer has full responsibility and control over the workload security, but also the highest cost and maintenance. On-premises deployment can offer more security and compliance than cloud deployment, depending on the customer's security posture and practices.
References:
https://www.cisco.com/site/us/en/products/security/secure-workload/index.html
https://www.checkpoint.com/cyber-hub/cloud-security/what-is-cloud-workload-security/
NEW QUESTION # 113
......
100% Guarantee Download 350-701 Exam Dumps PDF Q&A: https://www.itcertmagic.com/Cisco/real-350-701-exam-prep-dumps.html
Kickstart your Career with Real Updated Questions: https://drive.google.com/open?id=10DQL1HovLazjP3FZXsPKp7_v-XWZ1MDa