

[Full-Version] 2023 New 300-730 Actual Exam Dumps, Cisco Practice Test
Study HIGH Quality 300-730 Free Study Guides and Exams Tutorials
NEW QUESTION # 22
Which command automatically initiates a smart tunnel when a user logs in to the WebVPN portal page?
- A. auto-start
- B. auto-run
- C. auto-connect
- D. auto-upgrade
Answer: A
Explanation:
Section: Remote access VPNs
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/asa/asa91/configuration/vpn/ asa_91_vpn_config/webvpn-configure-policy-group.html
NEW QUESTION # 23
Which two NHRP functions are specific to DMVPN Phase 3 implementation? (Choose two.)
- A. resolution request
- B. resolution reply
- C. registration request
- D. registration reply
- E. redirect
Answer: B,E
NEW QUESTION # 24
Which VPN does VPN load balancing on the ASA support?
- A. VTI
- B. IPsec site-to-site tunnels
- C. L2TP over IPsec
- D. Cisco AnyConnect
Answer: D
Explanation:
Section: Secure Communications Architectures
NEW QUESTION # 25
Which configuration construct must be used in a FlexVPN tunnel?
- A. IKEv1 policy
- B. multipoint GRE tunnel interface
- C. EAP configuration
- D. IKEv2 profile
Answer: D
NEW QUESTION # 26
Which VPN solution uses TBAR?
- A. VTI
- B. Cisco AnyConnect
- C. DMVPN
- D. GETVPN
Answer: D
NEW QUESTION # 27
An engineer is configuring clientless SSL VPN. The finance department has a database server that only they should access, but the sales department can currently access it. The finance and the sales departments are configured as separate group-policies. What must be added to the configuration to make sure the users in the sales department cannot access the finance department server?
- A. smart tunnel
- B. webtype ACL
- C. tunnel group lock
- D. port forwarding
Answer: C
NEW QUESTION # 28
Which VPN technology must be used to ensure that routers are able to dynamically form connections with each other rather than sending traffic through a hub and be able to advertise routes without the use of a dynamic routing protocol?
- A. FlexVPN
- B. DMVPN Phase 3
- C. GETVPN
- D. DMVPN Phase 2
Answer: A
Explanation:
(FlexVPN supports the use of Dynamic Routing protocols such as EIGRP, BGP and OSPF. FlexVPN also has the ability to advertise routes in the IKEv2 SA's. In order to do this we must configure an IKEv2 Authorization Policy,)
NEW QUESTION # 29
Which feature allows the ASA to handle nonstandard applications and web resources so that they display correctly over a clientless SSL VPN connection?
- A. Smart Tunnel
- B. single sign-on
- C. WebType ACL
- D. plug-ins
Answer: A
Explanation:
Reference:
https://www.cisco.com/c/en/us/td/docs/security/asa/asa90/configuration/guide/asa_90_cli_config/ vpn_clientless_ssl.html#29951
NEW QUESTION # 30
A network engineer has almost finished setting up a clientless VPN that allows remote users to access internal HTTP servers. Users must enter their username and password twice: once on the clientless VPN web portal and again to log in to internal HTTP servers. The Cisco ASA and the HTTP servers use the same Active Directory server to authenticate users. Which next step must be taken to allow users to enter their password only once?
- A. Set up the Cisco ASA to authenticate users via a SAML 2.0 IDP.
- B. Use LDAPS and add password management to the clientless tunnel group.
- C. Create smart tunnels for the HTTP servers.
- D. Configure auto-sign-on using NTLM authentication.
Answer: D
NEW QUESTION # 31
Why must a network engineer avoid usage of the default X.509 certificate when implementing clientless SSLVPN on an ASA?
- A. The certificate is regenerated at each reboot.
- B. The certificate is too weak to provide adequate security.
- C. The default X.509 certificate is not supported for SSLVPN.
- D. The certificate must be managed by the local CA.
Answer: A
Explanation:
By default, the ASA generates a self-signed X.509 certificate upon startup. This certificate is used in order to serve client connections by default. It is not recommended to use this certificate because its authenticity cannot be verified by the browser. Furthermore, this certificate is regenerated upon each reboot so it changes after each reboot. https://www.cisco.com/c/en/us/support/docs/security-vpn/webvpn-ssl-vpn/119417-config-asa-00.html
NEW QUESTION # 32
Refer to the exhibit.
An engineer is building an IKEv1 tunnel to a peer Cisco ASA, but the tunnel is failing. Based on the configuration in the exhibit, which action must be taken to allow the VPN tunnel to come up?
- A. Change the transform set mode to transport.
- B. Enable IKEv1 on the outside interface.
- C. Change the IKEv1 policy number to be at least 256.
- D. Add a route for the 10.7.7.0/24 network to egress the outside interface.
Answer: B
NEW QUESTION # 33
Refer to the exhibit.
Which type of VPN is used?
- A. Cisco Easy VPN
- B. GETVPN
- C. clientless SSL VPN
- D. Cisco AnyConnect SSL VPN
Answer: A
NEW QUESTION # 34
Refer to the exhibit.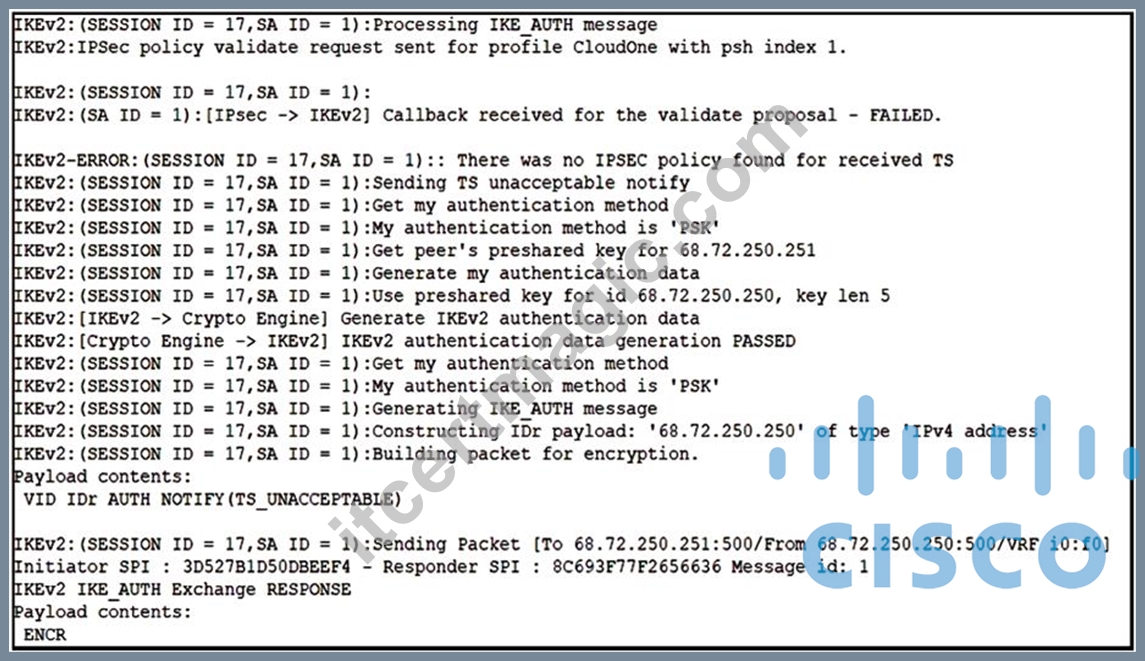
Based on the debug output, which type of mismatch is preventing the VPN from coming up?
- A. PFS
- B. interesting traffic
- C. preshared key
- D. lifetime
Answer: D
Explanation:
If the responder's policy does not allow it to accept any part of the proposed Traffic Selectors, it responds with a TS_UNACCEPTABLE Notify message.
NEW QUESTION # 35
In a FlexVPN deployment, the spokes successfully connect to the hub, but spoke-to-spoke tunnels do not form. Which troubleshooting step solves the issue?
- A. Verify the hub configuration to check if the NHRP shortcut is enabled.
- B. Verify the spoke configuration to check if the NHRP redirect is enabled.
- C. Verify that the spoke receives redirect messages and sends resolution requests.
- D. Verify that the tunnel interface is contained within a VRF.
Answer: C
NEW QUESTION # 36
A company's remote locations connect to the data centers via MPLS. A new request requires that unicast and multicast traffic that exits in the remote locations be encrypted. Which non-tunneled technology should be used to satisfy this requirement?
- A. SSL
- B. DMVPN
- C. FlexVPN
- D. GETVPN
Answer: D
NEW QUESTION # 37
An administrator is setting up AnyConnect for the first time for a few users. Currently, the router does not have access to a RADIUS server. Which AnyConnect protocol must be used to allow users to authenticate?
- A. EAP-AnyConnect
- B. EAP-GTC
- C. EAP-MD5
- D. EAP-MSCHAPv2
Answer: A
NEW QUESTION # 38
Refer to the exhibit.
Which value must be configured in the User Group field when the Cisco AnyConnect Profile is created to connect to an ASA headend with IPsec as the primary protocol?
- A. address-pool
- B. tunnel-group
- C. group-alias
- D. group-policy
Answer: B
Explanation:
The user group is used in conjunction with Host Address to form a group-based URL. If you specify the Primary Protocol as IPsec, the User Group must be the exact name of the connection profile (tunnel group). For SSL, the user group is the group-url of the connection profile. https://www.cisco.com/c/en/us/td/docs/security/vpn_client/anyconnect/anyconnect40/administration/guide/b_AnyConnect_Administrator_Guide_4-0/anyconnect-profile-editor.html#ID-1430-0000026c
NEW QUESTION # 39
A company is setting up a dynamic crypto map on the Cisco ASA at the headquarters to accept connections from the branch offices. There will be no IP subnet overlap between the branch offices, but the engineer does not know which encryption domains will be requested by the branch offices. Additionally, the company security policy states that routing protocol traffic should not leave the HQ network. Which solution should be used to route traffic back to the branches from the Cisco ASA with minimal administrative effort?
- A. Configure snapshot routing with EIGRP to send out of band routing updates.
- B. Configure a default route with the tunneled keyword on all branch routers.
- C. Configure Reverse Route Injection on the dynamic crypto map.
- D. Configure static routes for remote subnets.
Answer: C
NEW QUESTION # 40
A Cisco ASA is configured in active/standby mode. What is needed to ensure that Cisco AnyConnect users can connect after a failover event?
- A. Configure a backup server in the XML profile.
- B. AnyConnect images must be uploaded to both failover ASA devices.
- C. AnyConnect client must point to the standby IP address.
- D. The vpnsession-db must be cleared manually.
Answer: B
Explanation:
Section: Secure Communications Architectures
Explanation/Reference: https://www.cisco.com/c/en/us/td/docs/security/asa/asa90/configuration/guide/asa_90_cli_config/ ha_active_standby.html
NEW QUESTION # 41
Which parameter is initially used to elect the primary key server from a group of key servers?
- A. highest-priority value
- B. code version
- C. highest IP address
- D. lowest IP address
Answer: A
Explanation:
Reference:
https://www.cisco.com/c/en/us/products/collateral/security/group-encrypted-transport-vpn/ deployment_guide_c07_554713.html
NEW QUESTION # 42
Refer to the exhibit.
An engineer is diagnosing an issue that occurred after a router at a branch site was assigned a new address. Based on the debugs, what must be done to resolve this issue?
- A. Ensure that the UDP 500 packets between devices are not dropped.
- B. Ensure that the correct preshared keys are set on both sides.
- C. Add the remote peer's identity to the server's IKEv2 profile.
- D. Add the remote peer's IP address to the server's IKEv2 keyring.
Answer: C
NEW QUESTION # 43
A network engineer has been tasked with configuring SSL VPN to provide remote users with access to the corporate network. Traffic destined to the enterprise IP range should go through the tunnel, and all other traffic should go directly to the Internet. Which feature should be configured to achieve this?
- A. split-tunnel
- B. dual-homing
- C. hairpinning
- D. U-turning
Answer: A
NEW QUESTION # 44 
Refer to the exhibit. Cisco AnyConnect must be set up on a router to allow users to access internal servers
192.168.0.10 and 192.168.0.11. All other traffic should go out of the client's local NIC. Which command accomplishes this configuration?
- A. svc split include acl CCNP
- B. svc split exclude acl CCNP
- C. svc split exclude 192.168.0.0 255.255.255.0
- D. svc split include 192.168.0.0 255.255.255.0
Answer: A
Explanation:
Section: Secure Communications Architectures
Explanation/Reference:
NEW QUESTION # 45
Refer to the exhibit.
Cisco AnyConnect must be set up on a router to allow users to access internal servers 192.168.0.10 and 192.168.0.11. All other traffic should go out of the client's local NIC. Which command accomplishes this configuration?
- A. svc split include acl CCNP
- B. svc split exclude acl CCNP
- C. svc split exclude 192.168.0.0 255.255.255.0
- D. svc split include 192.168.0.0 255.255.255.0
Answer: A
NEW QUESTION # 46
......
Get 100% Real Free CCNP Security 300-730 Sample Questions: https://www.itcertmagic.com/Cisco/real-300-730-exam-prep-dumps.html
Download Cisco 300-730 Exam Dumps to Pass Exam Easily: https://drive.google.com/open?id=1q0GryoJLK0diOsXAXgzIhSzlRxQtoNtl