

FCP_GCS_AD-7.6 Dumps Special Discount for limited time Try FOR FREE
FCP_GCS_AD-7.6 Dumps for success in Actual Exam Nov-2025]
NEW QUESTION # 12
Refer to the exhibit.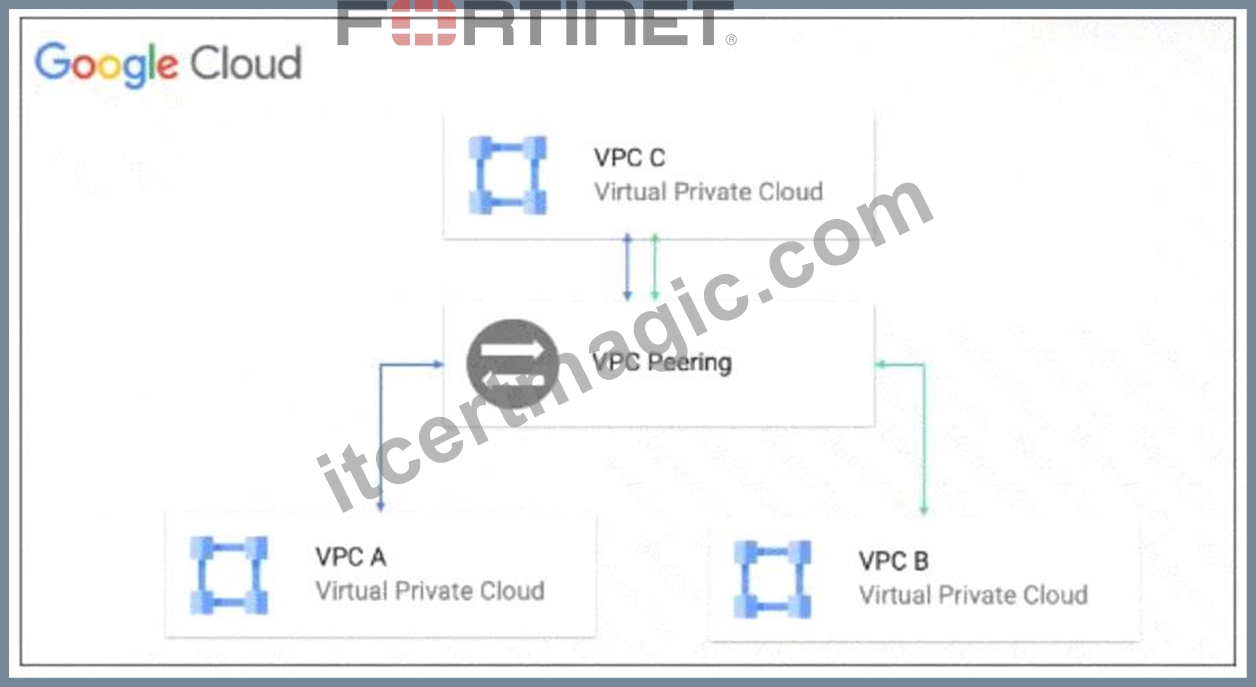
Which action must the administrator take to route traffic from VPC B to VPC A?
- A. The administrator must create a new VPC peering connection between VPC A and VPC B.
- B. The administrator must configure a custom route in VPC B and point the gateway to the VPC peering service.
- C. The administrator must deploy a FortiGate VM with at least three network interfaces.
- D. The administrative must configure a custom route in VPC B and point the gateway to VPC A.
Answer: C
Explanation:
Because VPC peering is non-transitive, traffic cannot route from VPC B to VPC A via VPC C. To enable routing between VPC A and VPC B through VPC C, a FortiGate VM with multiple network interfaces can act as a firewall/router to manage traffic between the three VPCs.
NEW QUESTION # 13
Your organization is deciding between deploying FortiGate active-passive high-availability (HA) in Google Cloud using either the software-defined network (SDN) connector or load balancers.
What two reasons should your organization choose the SDN connector over the load balancer deployment?
(Choose two.)
- A. There isess administrative overhead.
- B. Cost is lower.
- C. Failovers are faster because of to API calls.
- D. The SDN connector supports multizone failover.
Answer: A,B
Explanation:
Using the SDN connector avoids additional load balancer costs, making it more cost-effective.
The SDN connector enables multizone failover by directly managing network routing, which load balancers do not inherently support.
NEW QUESTION # 14
Refer to the exhibit.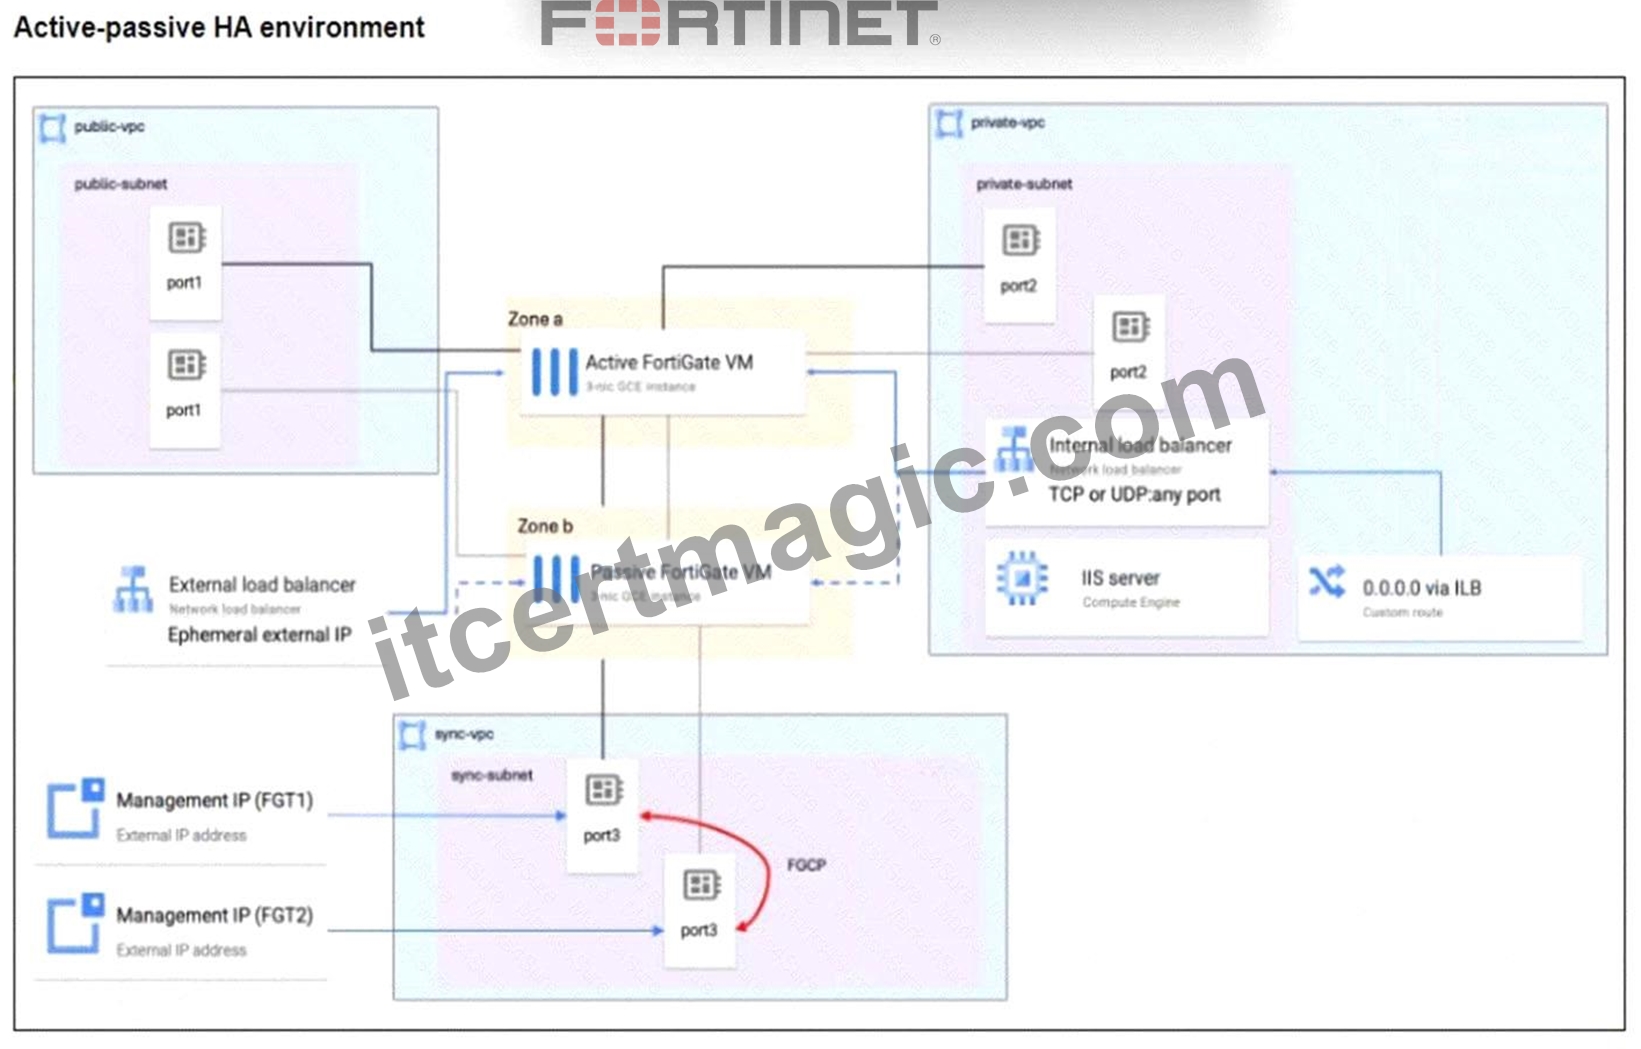
Which three things happen during a failover in which the passive FortiGate VM becomes the master cluster member in an active-passive high-availability (HA) environment? (Choose three.)
- A. The custom route is updated using API calls to forward all traffic to port2 of the new active cluster member device.
- B. The Management IP address moves from port3 of the current active member to port3 of the new active cluster member.
- C. The health check ensures that incoming traffic to the ephemeral external IP address of the load balancer is forwarded to the new active cluster member.
- D. The health check for the passthrough load balancers forces internal traffic to route to port2 of the new active cluster member.
- E. The health check status will indicate that the old active cluster member is unhealthy.
Answer: A,C,E
Explanation:
The load balancer health check detects the failure of the old active member and forwards traffic to the new active member.
The health check reflects the status change, marking the previous active as unhealthy.
API calls update custom routes to redirect traffic to the new active cluster member's internal interface (port2).
NEW QUESTION # 15
An organization has decided to deploy an active-active high-availability cluster in Google Cloud.
Which three load balancing features are critical to the successful deployment of the cluster? (Choose three.)
- A. The L3_DEFAULT protocol in the forwarding rule of the internal passthrough network load balancer
- B. The forwarding rule for the internal passthrough network load balancer as the next hot for custom routes
- C. The session termination of the external passthrough network load balancer
- D. The health check used by the internal and the external passthrough network load balancer
- E. The symmetric hashing of the internal passthrough network load balancer
Answer: B,D,E
Explanation:
Health checks ensure load balancers route traffic only to healthy cluster members.
Forwarding rules act as next hops in routing, directing traffic appropriately within the HA cluster.
Symmetric hashing ensures consistent and balanced traffic distribution across cluster members, critical for active-active deployments.
NEW QUESTION # 16
An organization is deploying an active-passive high availability (HA) cluster using passthrough load balancers in Google Cloud.
What is a critical factor for ensuring successful HA formation, failover, and traffic flow?
- A. There can be more than two cluster members.
- B. VDOM exceptions must be configured.
- C. Unicast FortiGate Clustering Protocol (FGCP) must be used.
- D. Incoming traffic must be source NATed to ensure traffic flow symmetry.
Answer: D
Explanation:
Source NAT ensures that traffic is symmetric by keeping the source IP consistent, which is critical for proper failover and session synchronization in an active-passive HA cluster using passthrough load balancers.
NEW QUESTION # 17
Your organization is deciding between deploying FortiGate active-passive high-availability (HA) in Google Cloud using either the software-defined network (SDN) connector or load balancers.
What two reasons should your organization choose the SDN connector over the load balancer deployment?
(Choose two.)
- A. There isess administrative overhead.
- B. Cost is lower.
- C. Failovers are faster because of to API calls.
- D. The SDN connector supports multizone failover.
Answer: A,B
Explanation:
Using the SDN connector avoids additional load balancer costs, making it more cost-effective.
The SDN connector enables multizone failover by directly managing network routing, which load balancers do not inherently support.
NEW QUESTION # 18
Refer to the exhibit.
Which three conclusions can you draw from the Google Cloud custom route? (Choose three.)
- A. A group-based passthrough network load balancer was created.
- B. The next hop must be updates manually in the custom route if the current next hop goes down.
- C. A health check was created.
- D. Atarget pool-based passthrough network load balancer was created.
- E. At least one instance group was created.
Answer: B,C,E
Explanation:
The route's next hop is a forwarding rule for a backend service, which indicates a group-based passthrough load balancer.
Group-based load balancers require health checks to monitor instance health.
Backend services attach to instance groups to distribute traffic, so at least one instance group exists.
NEW QUESTION # 19
Refer to the exhibit.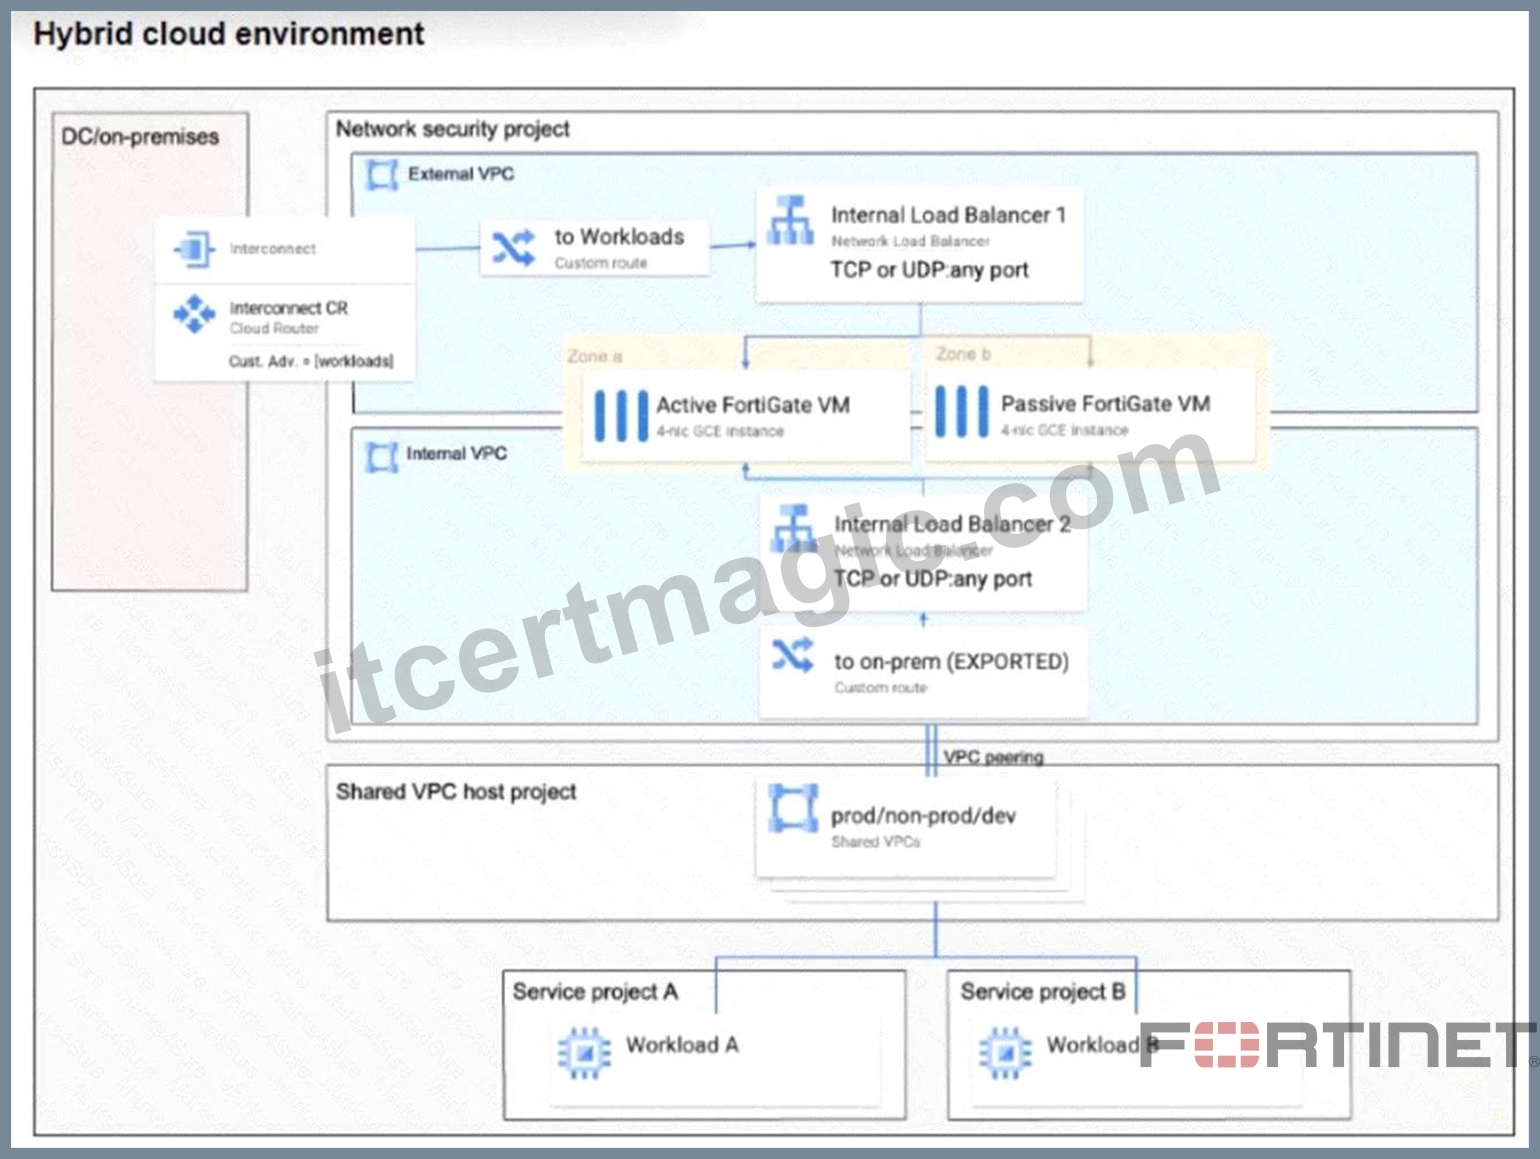
In this hybrid environment, in which two ways does the traffic flow from a network node in the on-premises network to Workload B in Google Cloud? (Choose two.)
- A. Once the traffic has been inspected, the active FortiGate uses VPC peering to forward the traffic to the Server project A VPC.
- B. When the packet reaches the external VPC, it is forwarded to the active FortiGate cluster member using a custom static route.
- C. Traffic will not reach the FortiGate devices because both load balancers are internal.
- D. Traffic will be routed using VPC peering from the Internal VPC to the destination subnet.
Answer: B,D
Explanation:
Traffic from on-premises enters the external VPC and is routed to the active FortiGate VM via custom routes for inspection.
After inspection, traffic is routed through VPC peering from the internal VPC to the service project subnet where Workload B resides.
NEW QUESTION # 20
You are tasked with deploying a load balancer in Google Cloud that does not terminate sessions arriving from outside the VPC and that forwards traffic to the organization's internal web servers.
Which load balancer type should you deploy?
- A. Proxy network load balancer
- B. External passthrough load balancer
- C. External application load balancer
- D. Internal passthrough load balancer
Answer: B
Explanation:
An external passthrough load balancer forwards traffic without terminating sessions, preserving the original client connection, which is ideal for forwarding traffic directly to internal web servers.
NEW QUESTION # 21
Refer to the exhibit.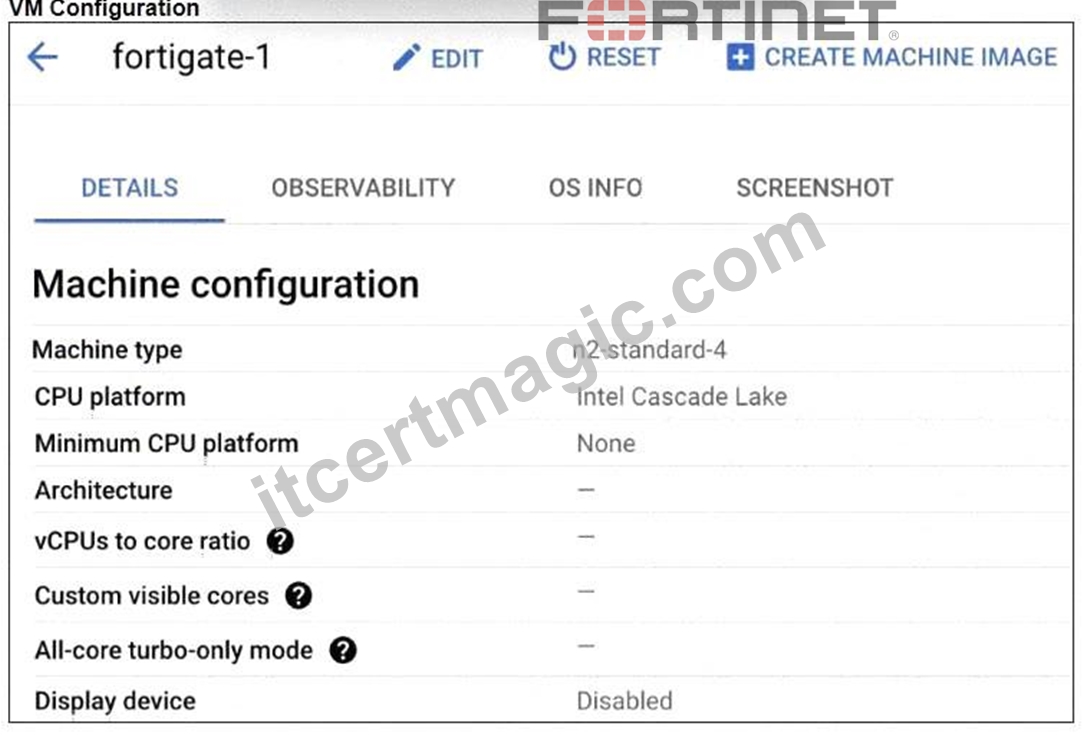
An organization has four virtual private cloud networks and deployed a FortiGate to protect the VPCs.
FortiGate is configured with four network interfaces and each network interface is assigned one of the four VPCs.
The organization is expanding and plans to add two more VPCs.
Which two options can the organization use to support the two new VPCs? (Choose two.)
- A. Modifying the FortiGate configuration to add two more network interfaces
- B. Utilizing VPC peering
- C. Adding a second FortiGate and configuring both FortiGate devices as an active-active high-availability cluster.
- D. Deleting FortiGate and replacing it with a Google Cloud machine type that supports six network interfaces
Answer: B,C
Explanation:
VPC peering allows connectivity between multiple VPCs without needing additional interfaces on FortiGate, enabling the existing FortiGate to protect multiple VPCs beyond its physical interface limits.
Adding a second FortiGate and configuring active-active HA enables scaling network protection for more VPCs by distributing traffic across multiple FortiGate instances, overcoming the network interface limit per VM.
NEW QUESTION # 22
Your organization has decided to deploy a high-availability (HA) cluster. One kye requirement of the deployment is to support configuration synchronization.
Which three deployment types should be considered? (Choose three.)
- A. Active-passive HA using passthrough load balancers
- B. Active-passive HA using software-defined networking (SDN)
- C. Active-passive HA using FGSP
- D. Active-active HA using auto scaling
Answer: A,B,C
Explanation:
These three deployment types support configuration synchronization between HA cluster members, which is critical for maintaining consistent state and seamless failover.
NEW QUESTION # 23
A cloud administrator is tasked with protecting web applications hosted in Google Cloud.
Which three cloud offerings can the administrator use to accomplish the task? (Choose three.)
- A. Google Cloud Armor
- B. Google Cloud Run
- C. FortiWeb VM
- D. Google Cloud IAM
- E. FortiWeb Cloud
Answer: A,C,E
Explanation:
FortiWeb VM is a web application firewall (WAF) deployed on Google Cloud to protect web apps.
Google Cloud Armor provides DDoS and application-level protection.
FortiWeb Cloud offers cloud-native WAF services to protect applications hosted in Google Cloud.
NEW QUESTION # 24
Refer to the exhibit.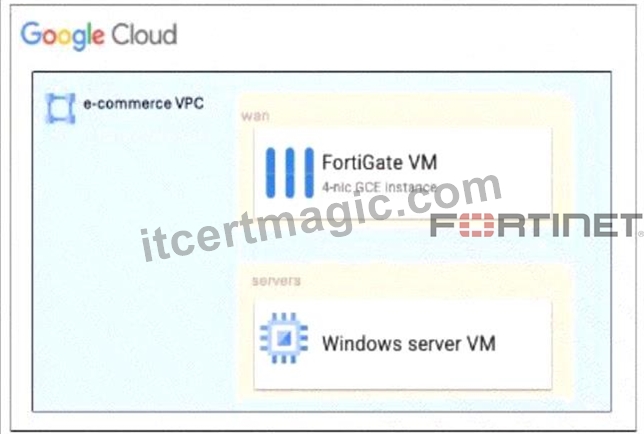
An administrator is troubleshooting network connectivity issues between two VMs deployed in Google Cloud.
One VM is a FortiGate located in the subnet "wan" that is part of the VPC "e-commerce". The other VM is a Windows server located in subnet "servers", which is also in the "e-commerce" VPC.
What are two reasons you cannot pint the Windows server from FortiGate? (Choose two.)
- A. The Windows firewall is blocking the traffic.
- B. The default Google Cloud firewall policy does not allow this traffic.
- C. Add a Google Cloud firewall rule to allow ICMP traffic inbound to the Windows firewall VM.
- D. ICMP traffic is blocked between Google Cloud subnets by default.
Answer: A,C
Explanation:
Google Cloud firewall rules are stateful and, by default, do not allow ICMP traffic; you must explicitly allow ICMP inbound traffic to the Windows VM.
The Windows VM's own firewall might block ICMP traffic, preventing ping responses.
NEW QUESTION # 25
An organization is planning to deploy two FortiGate VMs in two different regions.
Which two Google Cloud core components can span both FortiGate VMs in both regions? (Choose two.)
- A. Google Cloud project
- B. Google Cloud subnet
- C. Google Cloud virtual private cloud
- D. Google Cloud zone
Answer: A,C
Explanation:
A Google Cloud VPC can span multiple regions, allowing FortiGate VMs in different regions to be part of the same network.
A Google Cloud project provides the administrative boundary that can include resources across multiple regions and VPCs, enabling centralized management of both FortiGate VMs.
NEW QUESTION # 26
A cloud administrator has been receiving reports of slow response times from users accessing their organization's web application, which is protected by FortiWeb Cloud.
Which two steps can be taken to potentially alleviate the problem? (Choose two.)
- A. Changing the DNS records to point to the web application.
- B. Adding additional passthrough load balancers.
- C. Deploying FortiWeb Cloud in the same region where the web application is hosted.
- D. Enabling the content delivery network (CDN).
Answer: C,D
Explanation:
Deploying FortiWeb Cloud closer to the web application reduces latency and improves response times.
Enabling CDN caches content closer to users, reducing load times and speeding up content delivery.
NEW QUESTION # 27
......
Accurate FCP_GCS_AD-7.6 Answers 365 Days Free Updates: https://www.itcertmagic.com/Fortinet/real-FCP_GCS_AD-7.6-exam-prep-dumps.html
Realistic FCP_GCS_AD-7.6 100% Pass Guaranteed Download Exam Q&A: https://drive.google.com/open?id=12J4pHFVRs5bMp0uGquPWyh5vwXQ82OAb